Criminals Are Running a Crypto Theft Operation Out of a Public Google Spreadsheet


Hiding in Plain Sight
Attackers no longer need to build suspicious infrastructure. That’s the worrying finding from the latest study by Cisco’s threat intelligence organisation, Talos. Following two campaigns Talos has now documented, the operations sit inside services that companies already trust and allow through the firewall, which is exactly what makes them so difficult to spot.
"Almost every organization on earth allows traffic to Google Docs," says Jan Heijdra, Field CTO Security at Cisco Benelux. "So, if you can keep your attack code in a spreadsheet, you get free, reliable hosting that nobody blocks and nobody questions. There's no strange domain to flag, no odd server to trace. You're looking at a document request, and that's all your logs will tell you."
Stealing Crypto Through the Browser
The first campaign has been running since October 2025 and targets cryptocurrency traders. The bait is a fake leaked security report claiming a flaw at two currency swap sites that would pay out a bonus of 25% or more. It is designed to attract people willing to exploit a bug they don't really understand. Talos found it circulating on Telegram, on criminal forums and on text-sharing sites.
Victims are told to paste JavaScript into the Chrome address bar or add it to a legitimate browser add-on so it reloads every visit. That pasted snippet is only a fetcher. The part that makes the attack hard to catch is where the real code lives: a publicly published Google spreadsheet, retrieved through a Google feature dating back to 2008. The operators even hid it in the sheet as white text on a white background.
What arrives is a skimmer, the digital version of a card reader glued to a cash machine. It rewrites the deposit address shown on the trading page, replaces any address the victim copies, and paints a convincing fake "bonus" onto the screen.
Talos traced 49 Bitcoin addresses, of which 24 collected victim funds worth at least roughly 10,000 US dollars, then laundered them through more than 3,000 further addresses. The true figure is likely higher, as Talos could not recover samples from the earliest phase. After Talos shared its findings with Google and the affected sites in April, the lure and control documents were taken down. Around a week later the campaign was running again from a new spreadsheet, and Talos reports that later versions have stayed active into August despite being flagged repeatedly.
From Fake CAPTCHA to Hands-On Access
The second case began in April 2026 with unusual activity at a Ukrainian government organization. Talos assesses with moderate confidence that this was part of a broad crypto and credential theft operation rather than an attack on that organization specifically.
The pattern repeats, with different cover. Malicious code planted on a compromised website, in an infection chain linked to ClearFake, pulls its next instructions from a public blockchain, another service that is trusted and effectively impossible to take down. The victim then sees a fake Google CAPTCHA, the checkbox that normally proves you are not a robot, and is told to paste a command into Windows. That installs a stealer known as Amatera, which harvests browser data, messaging apps, more than 100 cryptocurrency wallets, password managers and files containing private keys. Follow-on payloads shut down security software, turn the machine into a relay for the attacker's traffic, and install a hidden copy of a commercial remote support tool. Its control server sat on an IP address in Russia. On that basis, Talos assesses with moderate confidence that a Russian threat actor ran this part of the activity.
What To Do
Most organizations are not the target here. The methods are the concern, because the same approach could be turned on almost any customer-facing website.
"The lesson isn't to distrust Google," Heijdra says. "It's that 'the destination is trusted' has stopped being a useful signal. You need to ask which application is making the request and whether that makes any sense."
He recommends three steps. Manage the browser like you manage the laptop, controlling which extensions staff can install. Watch for requests to cloud collaboration services from applications or browser sessions that have no reason to make them and check the third-party components running in your own customer-facing sites for anything that looks out of place. And add one simple rule to your awareness training: nothing legitimate ever asks you to copy a command and run it to prove you are human.
Both reports include detection guidance and technical indicators for security teams.
Article Enquiry
Email Article
Save Article
Feedback
To advertise email advertising@creamermedia.co.za or click here
Projects
Latest Multimedia
Latest News
Showroom
FLANDERS Southern Africa provides integrated solutions for mining and industrial operations, covering field services, automation, electrification,...
VISIT SHOWROOM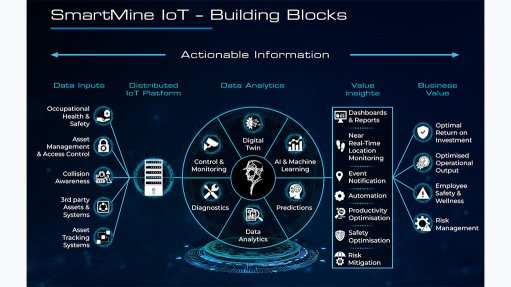
SmartMine IoT has been developed with the mining industry in mind, to provides our customers with powerful business intelligence and data modelling...
VISIT SHOWROOM
Announcements
What's On
Subscribe to improve your user experience...
Option 1 (equivalent of R125 a month):
Receive a weekly copy of Creamer Media's Engineering News & Mining Weekly magazine
(print copy for those in South Africa and e-magazine for those outside of South Africa)
Receive daily email newsletters
Access to full search results
Access archive of magazine back copies
Access to Projects in Progress
Access to ONE Research Report of your choice in PDF format
Option 2 (equivalent of R375 a month):
All benefits from Option 1
PLUS
Access to Creamer Media's Research Channel Africa for ALL Research Reports, in PDF format, on various industrial and mining sectors
including Electricity; Water; Energy Transition; Hydrogen; Roads, Rail and Ports; Coal; Gold; Platinum; Battery Metals; etc.
Already a subscriber?
Forgotten your password?
Receive weekly copy of Creamer Media's Engineering News & Mining Weekly magazine (print copy for those in South Africa and e-magazine for those outside of South Africa)
➕
Recieve daily email newsletters
➕
Access to full search results
➕
Access archive of magazine back copies
➕
Access to Projects in Progress
➕
Access to ONE Research Report of your choice in PDF format
RESEARCH CHANNEL AFRICA
R4500 (equivalent of R375 a month)
SUBSCRIBEAll benefits from Option 1
➕
Access to Creamer Media's Research Channel Africa for ALL Research Reports on various industrial and mining sectors, in PDF format, including on:
Electricity
➕
Water
➕
Energy Transition
➕
Hydrogen
➕
Roads, Rail and Ports
➕
Coal
➕
Gold
➕
Platinum
➕
Battery Metals
➕
etc.
Receive all benefits from Option 1 or Option 2 delivered to numerous people at your company
➕
Multiple User names and Passwords for simultaneous log-ins
➕
Intranet integration access to all in your organisation